Enterprise TPRM

Evidence-Based Third-Party Risk Management

Third-Party risk still runs on questionnaires and point-in-time reviews. With Anecdotes, dedicated agents run the full vendor lifecycle on real evidence: discovering vendors, verifying claims, and scoring risk against your standards. You set the rules, the agents do the work.
Smart Setup & Discovery

Launch a tiered program in under an hour, then surface the vendors already in use across your stack.

Agentic Assessment Pipeline

Agents enrich, classify, collect evidence, assess, and score every vendor on real evidence.

A Live View of Vendor Risk

Portfolio-wide posture, exception-only review, and always-on agents that keep every vendor current.

Third-Party Risk runs on the same continuously collected, audit-grade data as the rest of your GRC program, applied to the vendor context with intelligent workflows built for third-party risk.

Smart Setup & Discovery

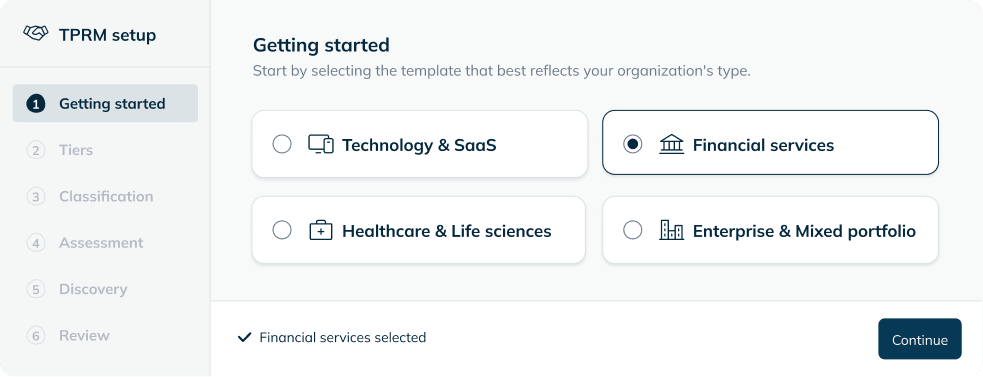
Live in Under an Hour

Choose an industry preset, review the tiers, rules, and questions it loads, and launch a working program in under an hour. Then let Discovery surface the third parties already in use across your stack, including the long tail of smaller vendors that usually goes unmanaged.

Key Features

Industry Presets & Configurable Tiers

Start from presets built for specific industries, each on its own reassessment cadence.

Your Questions, Your Way

Use preset per-tier question sets or upload your own. The questions stay; the manual, self-attested questionnaire goes.

AI-Assisted Configuration

Describe a classification rule in plain language and AI converts it into structured logic, with conflict detection so rules never contradict each other.

Vendor Discovery

Surface vendors automatically through the plugins already in your environment, with weekly auto-sync, deduplication, and add-by-name or chat.

Agentic Assessment Pipeline

Evidence-Based Assessment, End to End

Every vendor runs through a continuous, per-vendor pipeline of dedicated agents. Each does real work and hands off to the next, so a vendor goes from discovered to scored without manual assembly, and every answer traces back to a source.

Enrichment

Builds the vendor's initial profile and pulls in the data needed for classification and assessment.

Classification

Evaluates the vendor against your tier logic, answers the classification questions, and assigns the matching tier.

Collection

Determines which documents are in scope, fetches public ones, requests private ones, and validates each as it arrives.

Assessment

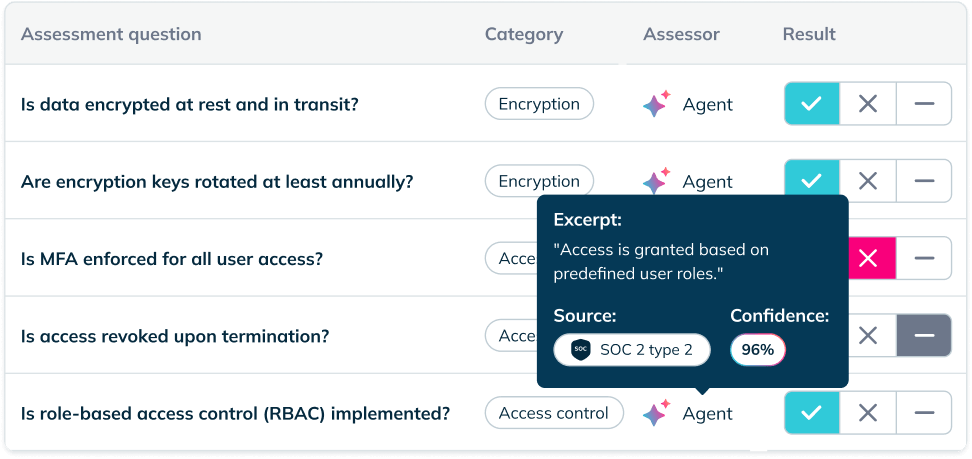
Completes a tier-based security assessment using your question sets, with traceable evidence for every answer.

Risk Score

Generates a context-aware residual risk score with a written explanation of what drove it up or down.

Key Features

Answers Backed by Evidence

Each question is answered Pass or Fail with the supporting document, section, and a confidence score.

Explainable Scores

Every score comes with a written rationale, so it is transparent and defensible to auditors, leadership, and the business.

Residual risk is scored against your tiers, questions, and evidence, not a universal benchmark.

Evidence, Not Self-Attestation

Answers come from ISO certificates, SOC 2 reports, trust centers, and other verifiable sources, rather than vendor-filled forms.

A Live View of Vendor Risk

Third-Party Risk You Can See, Review, and Trust to Stay Current

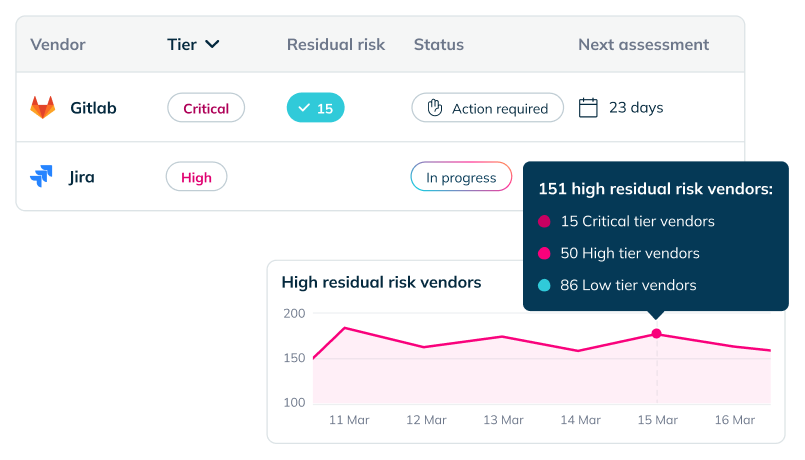
Your program is a living view of third-party risk, not a stack of completed forms. See portfolio-wide posture at a glance, drill into any vendor for the full record, act only where judgment is needed, and let background agents keep every vendor current.

Key Features

Filter the portfolio by tier, score, status, and next assessment, then open any vendor for the full audit record: classification reasoning, per-question evidence, findings, and history.

TPRM Chat

Query your portfolio, kick off an assessment, add a vendor, or review a decision, all in one thread. Chat is the shared surface where the TPRM team and Anecdotes’ TPRM agents ask, act, and decide together.

A prioritized queue surfaces only the decisions that need a person, customized to the needs of the team. Human-in-the-loop by design, not by default.

Always-On Agents

Background agents track reassessment timelines, monitor for expired documents, and recalculate risk when evidence changes, on the cadence you set per tier.

Build Custom Agents in Agent Studio

Automate Your Program's Specific Workflows

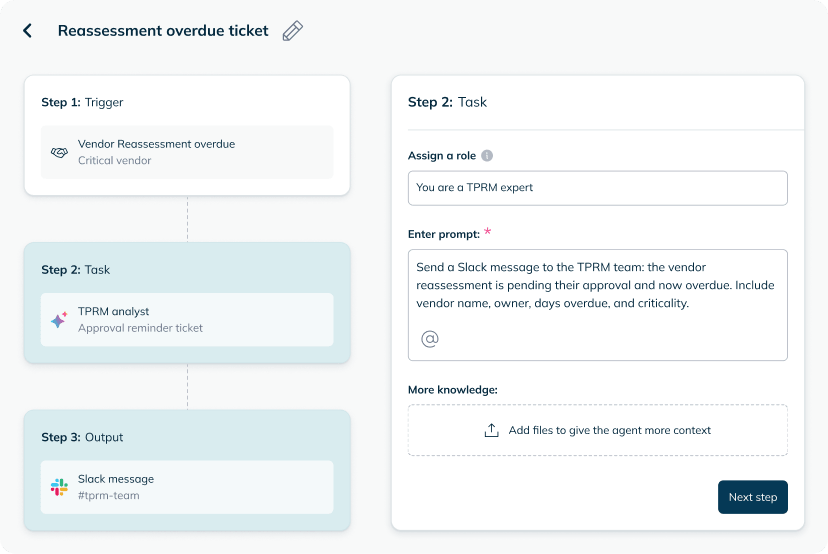
Use the Anecdotes Agent Studio to build agents that act on the events that matter to your program.

New critical finding
email the vendor owner with full context.
Reassessment overdue
send a Slack message to the TPRM team.
Score crosses threshold
route the vendor to the Action Hub for review.

One Platform for Compliance and Third-Party Risk

Third-Party Risk runs on the same Anecdotes Data Engine and risk register as your compliance program, already in production and continuously collecting audit-grade data from 230+ plugins. Vendor risk and compliance live on one platform and one audit-ready record, not in separate silos.

From Chasing Questionnaires to Verified Third-Party Risk

Stop scoring vendors on claims you can't verify. Start with a program where agents discover, verify, and score every vendor on real evidence, and keep your portfolio current. You set the rules, the agents do the work.

Frequently Asked Questions

How does the Anecdotes agentic assessment pipeline work?
What does each agent in the assessment pipeline do?
How does Anecdotes score vendor risk?
How does vendor discovery work?
How long does it take to set up a TPRM program in Anecdotes?
What are the main workspaces in Anecdotes TPRM?
How does Anecdotes keep vendor risk current after the first assessment?
How much of the work is automated versus reviewed by my team?