FedRAMP cr6

Get ready for FedRAMP CR26 with Anecdotes

Seamless migration to CR26.
Anecdotes helps you meet the new CR26 requirements by connecting to your existing systems, continuously validating evidence, and generating the structured outputs FedRAMP now requires.

CR26 is already here

A phased timeline for existing Rev5 authorizations.

DEC 7, 2026

VDR & VER

Mandatory (obtain & maintain)

New vulnerability management requirements with continuous coverage, faster remediation timelines and machine-readable reporting.

Explore VDR & VER

JAN 2027

Rules consolidation

Mandatory for Rev5 holders

Current Rev5 holders must adopt FedRAMP's consolidated rule updates.

MAR 7, 2027

Grace period ends

Revocation begins

The grace period for existing Rev5 authorizations to meet VDR & VER ends. Non-compliant certifications face revocation after this date.

JUN 2027

Rev5 sunset

Closed to new authorizations

Rev5 closes to new authorizations. FedRAMP 20x becomes the path forward for CSPs starting fresh.

Everything you need to run FedRAMP Rev5 under CR26

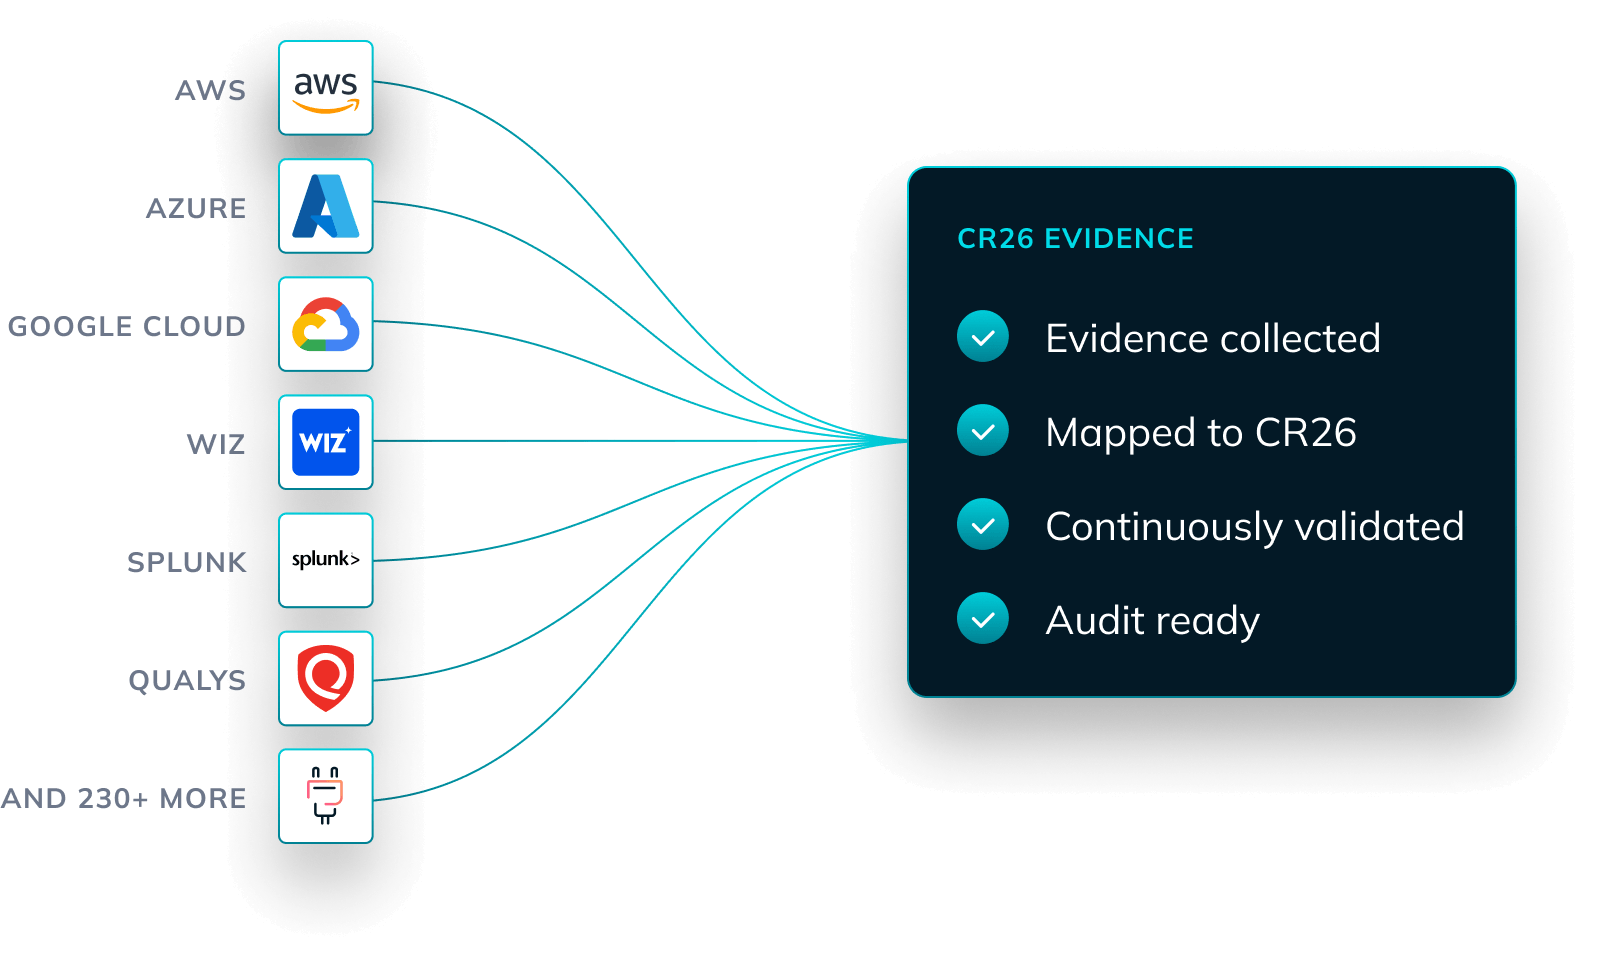
Anecdotes brings together your security and business systems, maps data to FedRAMP requirements, and helps you continuously validate compliance with the new CR26 rules.

Connect your systems

Bring evidence and security data directly from the source, structured so it can generate machine-readable compliance packages a reviewer can query. It's the same structured data that lets you automate FedRAMP reports instead of writing them.

Seamless Migration

Move from hand-written SSPs to the machine-readable 20x model without starting over. Existing Rev 5 documentation and the evidence behind it become inputs to your 20x preparation, not work you repeat.

No-Code GRC Agents

Automate your control validation, evidence collection, and remediation workflows without custom development. You configure the agents that collect and validate evidence inside the platform, without the engineering sprint, and every agent action stays explainable and owned by a person.

Trust Center Access

Your compliance posture in real time is available to assessors and agencies through Anecdotes' Trust Center. FedRAMP program status is ready to consume in both machine-readable and human-readable formats, and always reflects up-to-date control status.

Anecdotes vs. Single-Purpose Tool

What separates them is what happens after the badge: how evidence gets collected, how the SSP gets built, and whether the same platform can carry your commercial program too.
Anecdotes
Single-Purpose Tool
CCM & Evidence Collection
Native continuous evidence collection engine with a full CCM lifecycle: scoping, analysis, mitigation. Proven at scale with 150+ enterprises running commercial CCM on the same engine.
A point solution built around FedRAMP paperwork rather than continuous evidence. Evidence collection is narrower, and the CCM depth Anecdotes has built over years isn't there.
SSP Generation
Also automatically generates the SSP directly from the same live, continuously collected evidence, no separate tool or manual assembly required.
Generates SSP/POA&M documents effectively, its original core strength. But as FedRAMP shifts to continuous, rules-based validation, this is no longer a unique advantage.
Unified Platform (Commercial & Federal)
One platform for commercial and federal compliance today. Customers already run both on Anecdotes, with a single vendor and unified reporting.
Not built for commercial CCM at scale. The single-purpose tool partnered with Drata rather than build commercial capability itself. Federal and commercial live on separate tools.
Enterprise Fit
Built to fit complex environments (cloud, on-prem, and hybrid alike) with advanced data scoping that adapts to how your infrastructure actually looks, not a one-size-fits-all template.
Customers report friction with organizations that have existing authorizations, rigid control-narrative logic, and configs that don't flex across environments like multiple Okta instances.

Bottom line

Anecdotes is the only tool built with the native approach of modern FedRAMP (CR26/20x), and it still fits legacy Rev5 use cases. The single-purpose tool is a legacy tool built for initial SSP generation, and supports neither continuous monitoring nor commercial GRC use cases.

Don't rebuild your FedRAMP program. Build on it

You've already invested in your Rev5 authorization. Anecdotes gives you the data infrastructure to operate it under CR26 and be ready for what comes next.

230+

integrations

Enterprise grade

security and scale

Built for what's next

Rev5 today. 20x tomorrow.

Frequently Asked Questions

I'm Rev5 authorized. Do I have to migrate to 20x?
I am Rev5 High authorized. Can Anecdotes support me?
What's the difference between CR26 and FedRAMP 20x?
Do I need to rewrite my SSP for CR26?
What happens if I miss the December 7, 2026 deadline?
Can Anecdotes connect to my on-prem systems?
Trust Center Access