Staying on Rev5
Staying on Rev5
.png)
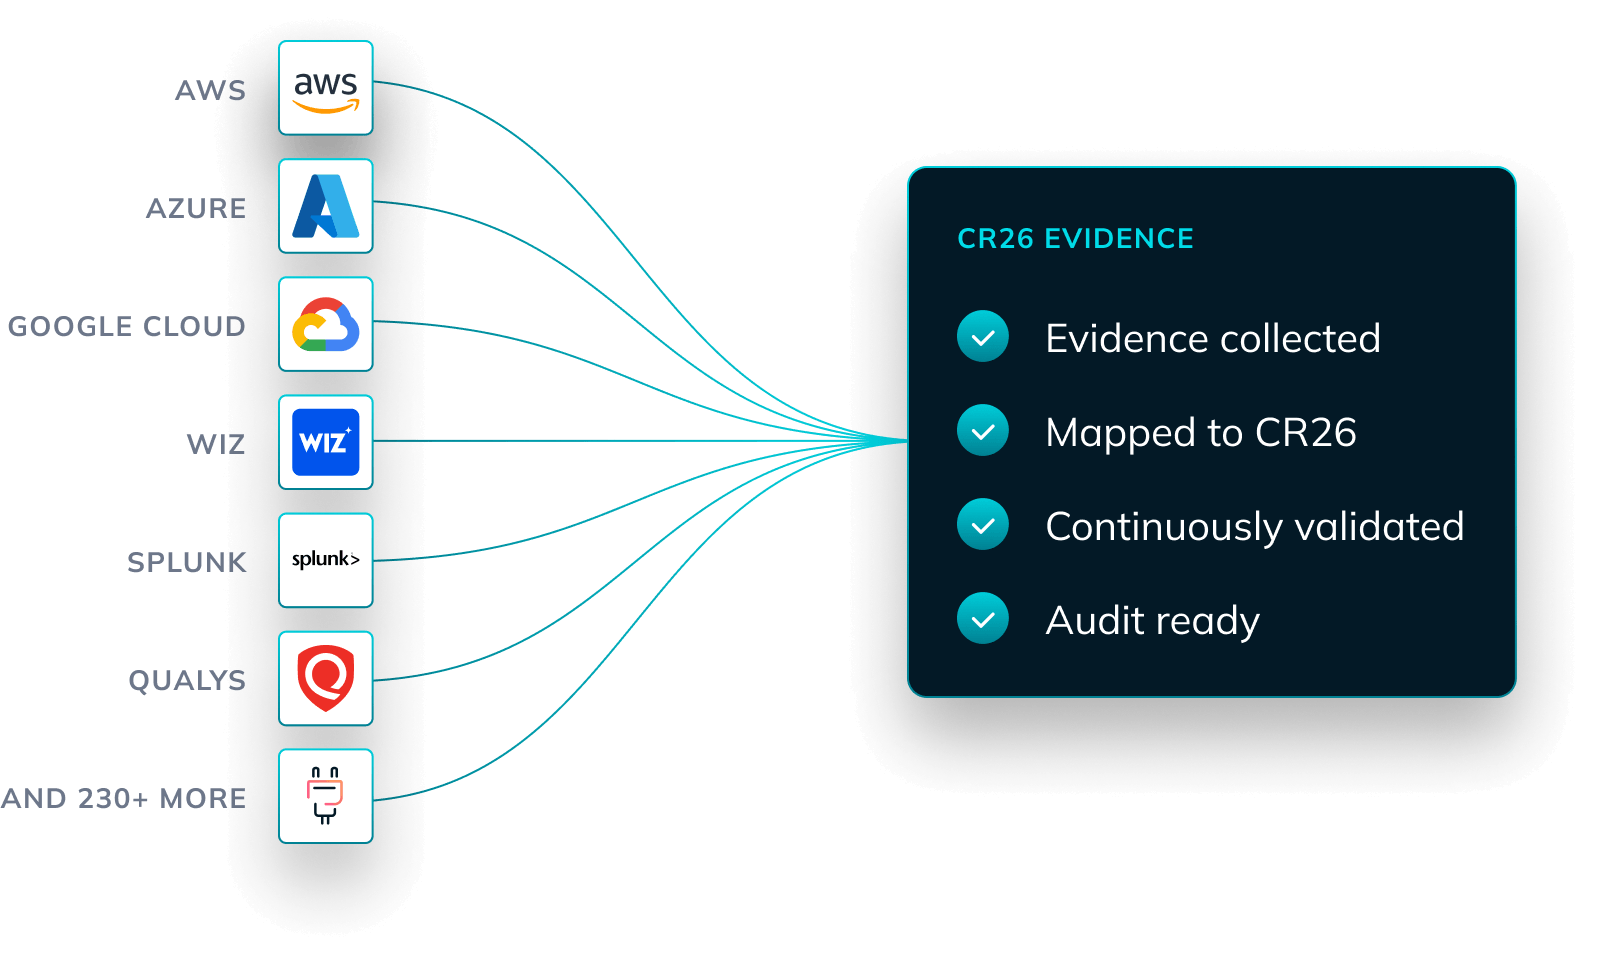
Bring evidence and security data directly from the source.
Link data to the NIST controls already in your Rev5 baseline.
Monitor and report on your compliance posture in real time through Anecdotes' dashboards. See current controls status between assessments, so "are we authorized right now?" has a live answer instead of a last-audit one.
The evidence you produce is assessment-ready for the 3PAOs already in the FedRAMP ecosystem, so validation runs on the data you maintained all along.
Continuous monitoring runs on the Rev5 authorization you already have. If you move to CR26 or 20x later, the same infrastructure carries over.
230+
integrations
Enterprise grade
security and scale
Built for what's next
Rev5 today. Whatever's next, tomorrow
Continuous monitoring catches drift before an assessor does, keeps your SSP and evidence current between audits, and puts you ahead if you decide to move to CR26 or 20x later. It's the same infrastructure either way.
No. Continuous monitoring layers on top of your existing Rev5 boundary and controls. Nothing about your authorization itself changes.
Not immediately. FedRAMP has signaled that Rev5 will eventually become a legacy process, so it's worth preparing for the shift. In the meantime, Anecdotes supports you either way: stay on Rev5 with continuous monitoring, or start building toward 20x when you're ready.
Yes. Anecdotes' Class C certification doesn't limit which agencies you can serve: the platform itself doesn't store high-regulated agency data, so it's available to FedRAMP High authorized companies as well.
Yes. Anecdotes runs the most advanced data engine in the industry and regularly connects to on-prem and private cloud environments, not just public cloud.
Absolutely. Anecdotes' plugin builder makes it easy to create custom plugins, so continuous monitoring extends to your unique, in-house systems too.