Wednesday, October 28 · 12:00 PM EST · Live
The security questionnaire was built for a world with a few dozen vendors, one or two
frameworks, and enough time to read what came back.
Then portfolios ran past a hundred vendors, and every tool that shipped an AI feature this
year re-tiered itself into your critical list. The questionnaires got longer. The answers
still come back as a column of yes. The proof that would settle it is sitting in an audit
report nobody has the hours to open. What changes when an agent can find that evidence, read it, understand what it proves, and assess it against your own requirements?
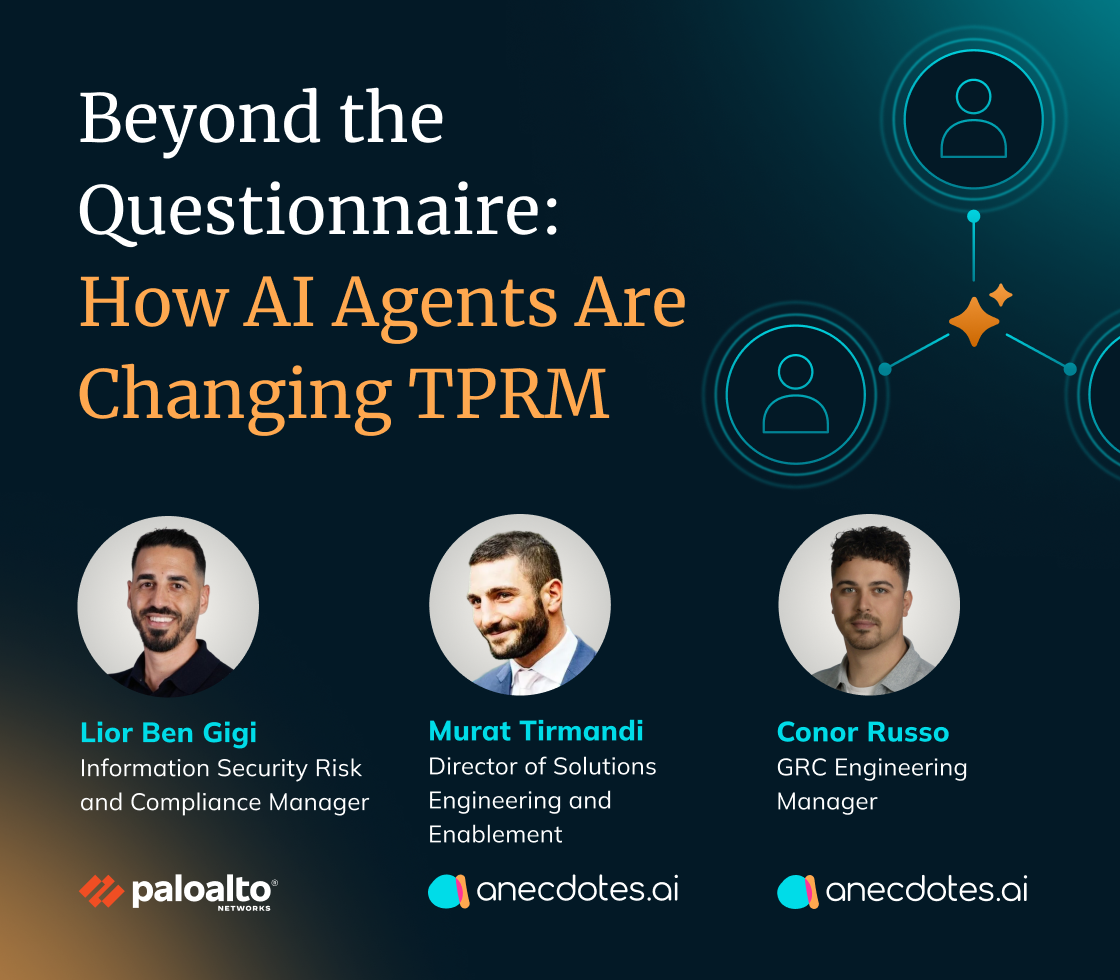
Murat Tirmandi opens on why the questionnaire model stopped holding, how work changes by introducing agents, and how Anecdotes approached TPRM differently. Then Conor Russo (ex Cyera, Netskope, Optiv), who now runs third party risk and GRC at Anecdotes, sits down with Lior who manages compliance and risk at Palo Alto Networks and Natalie who leads GRC at Fireworks AI, on what their programs used to entail, what their teams work on now, and what a strong TPRM practice takes. Conor closes with a short live walkthrough of his own program: one vendor, assessed against his own standard, on evidence rather than answers.
What you’ll take away
- What a defensible assessment has to show, now that “we sent the questionnaire” does not count as risk management
- Where a vendor review actually goes, and what a team gets back when collecting and reading stop being the job
- Why AI adoption re-tiered a portfolio you already assessed, and why headcount was never going to fix it
- The difference between speeding up the questionnaire and removing it, and where human judgment still sits
- What a strong practice requires now, and what to fix first if yours still runs on
questionnaires
If your board asked today which of your critical vendors meet your own standard, how long
would it take to answer with proof? Join us on October 28.