Security KPIs
Security KPIs,
measured not claimed.
Your view of your own security still moves at the speed of a quarterly report. Anecdotes computes your KPIs continuously from your own stack, so every number traces back to the record it came from.
83 tools
From 29 different vendors in the average enterprise, and no single one holds your program's number.
89 days
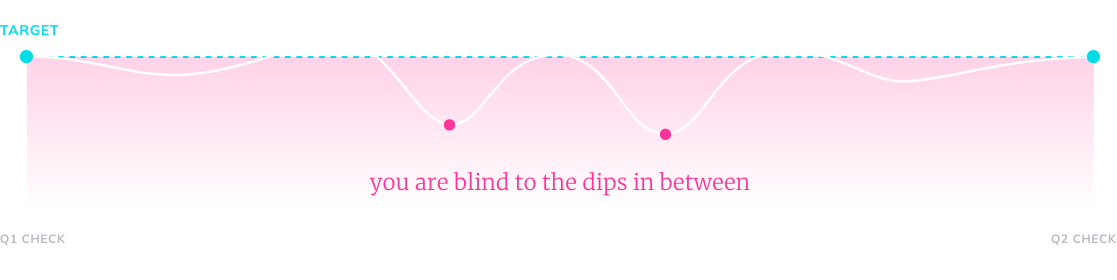
A security assumption can go unverified this long between quarterly snapshots.
29 min
Mean Time-to-Compromise (MTTC), while your own measurement refreshes only once a quarter.
Between two snapshots, coverage drifts unseen.
Five steps from your stack to the boardroom

01
KPI Definition
Your own metrics and thresholds, shaped with AI's help but never decided by AI.

02
Operational Integration
Your whole operating stack, connected automatically with no manual exports.

03
Continuous Evaluation
Computed continuously and deterministically, the same result from the same data every time.

04
AI Action
Custom agents and reports flag what changed, with every number traceable to the source record.

05
Business Context
Technical KPIs become a clear, board-level story.
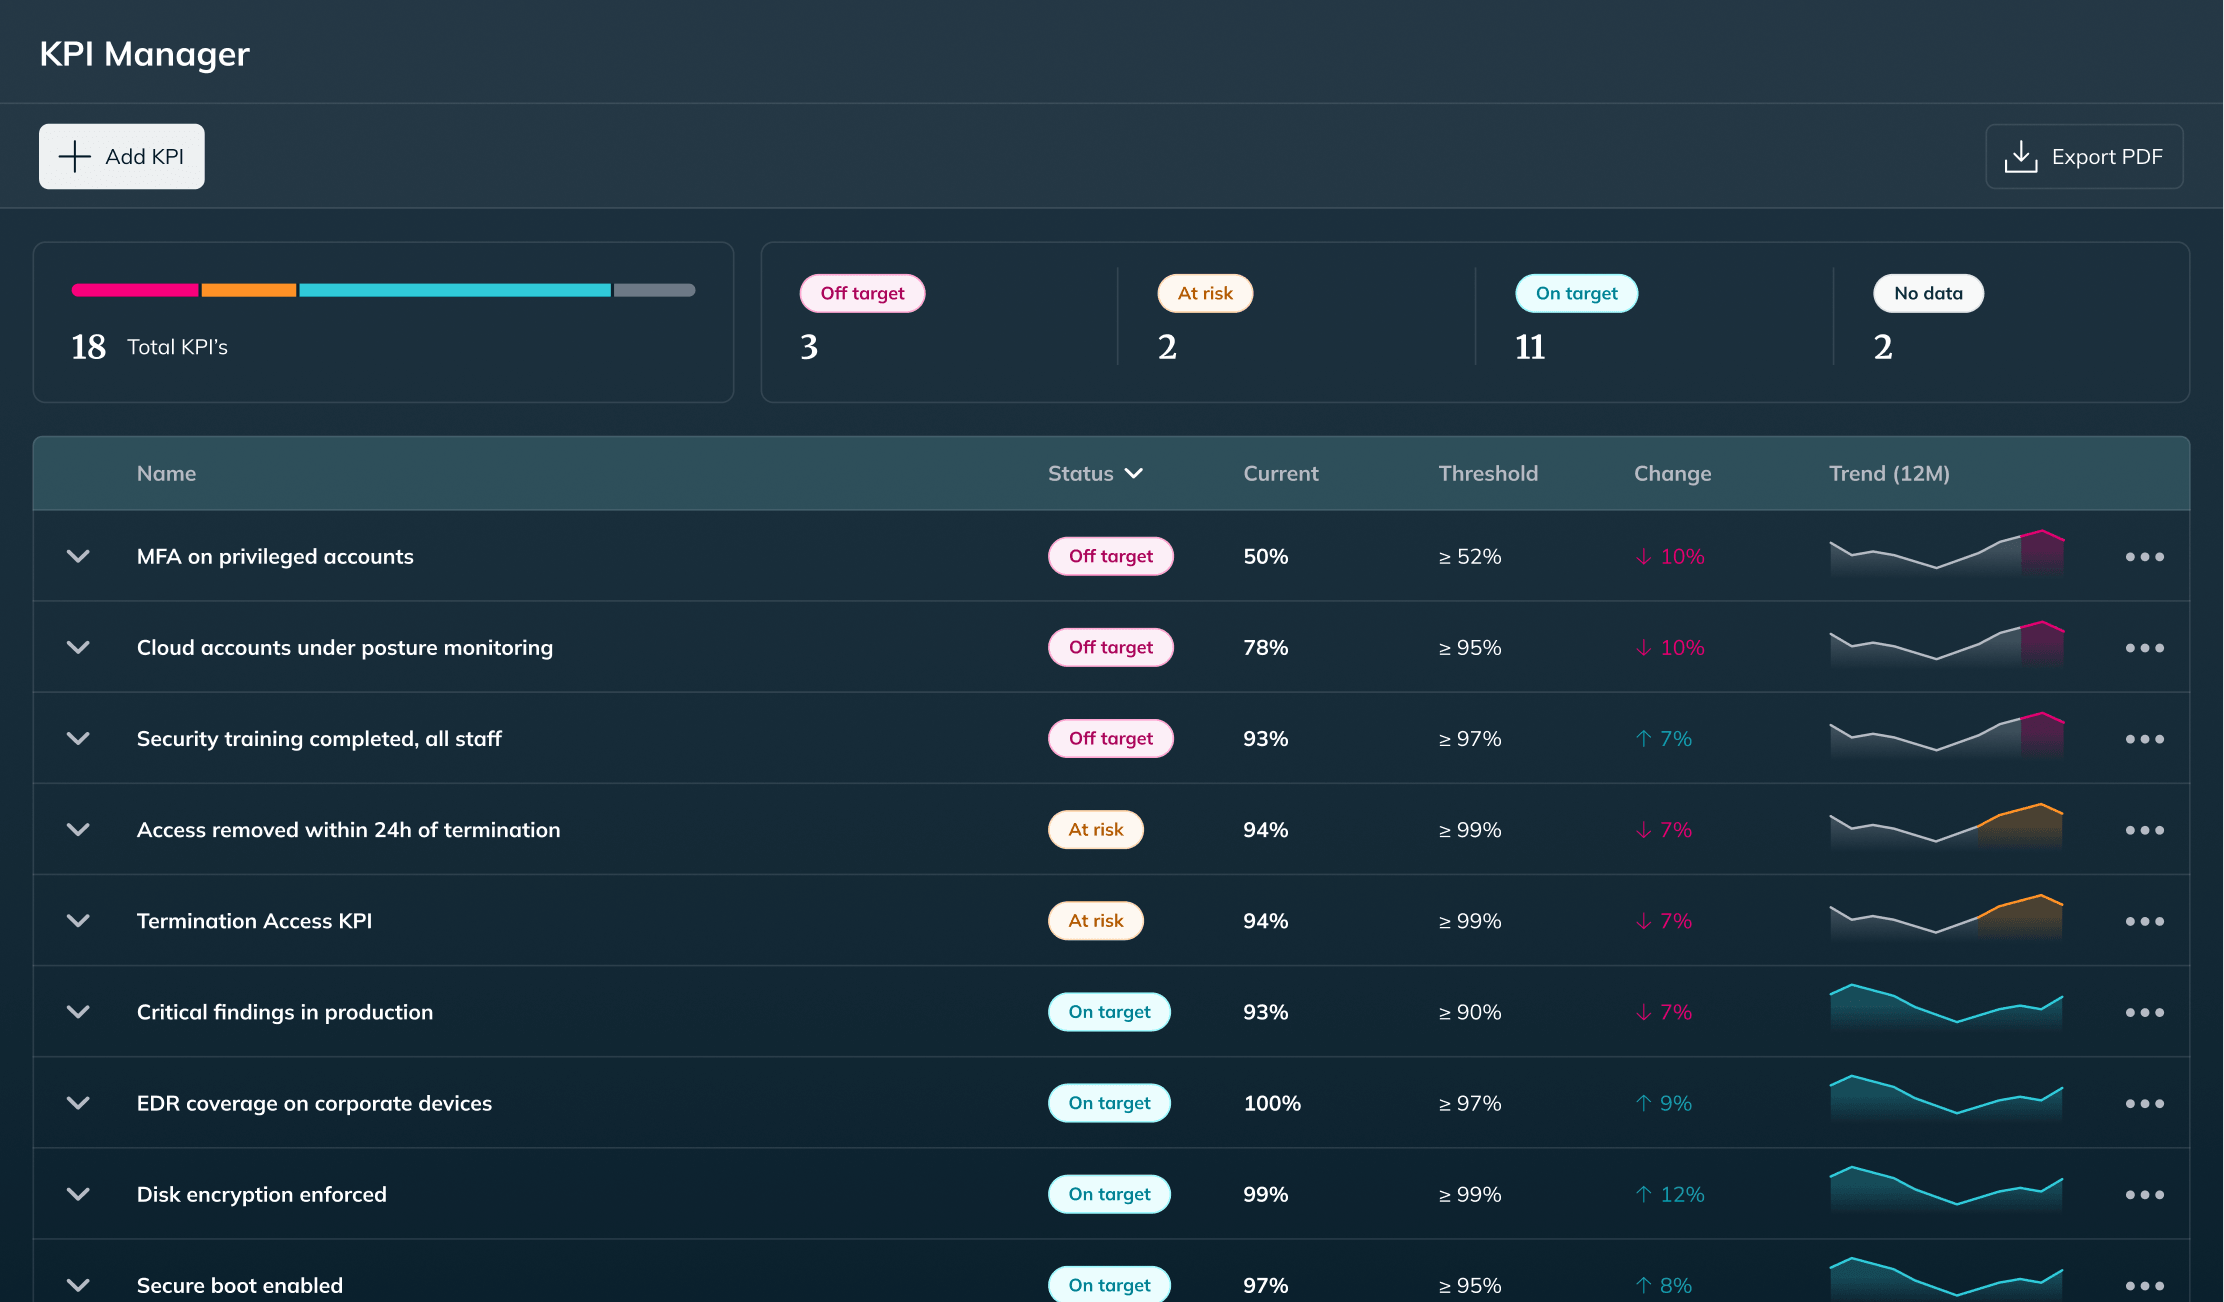
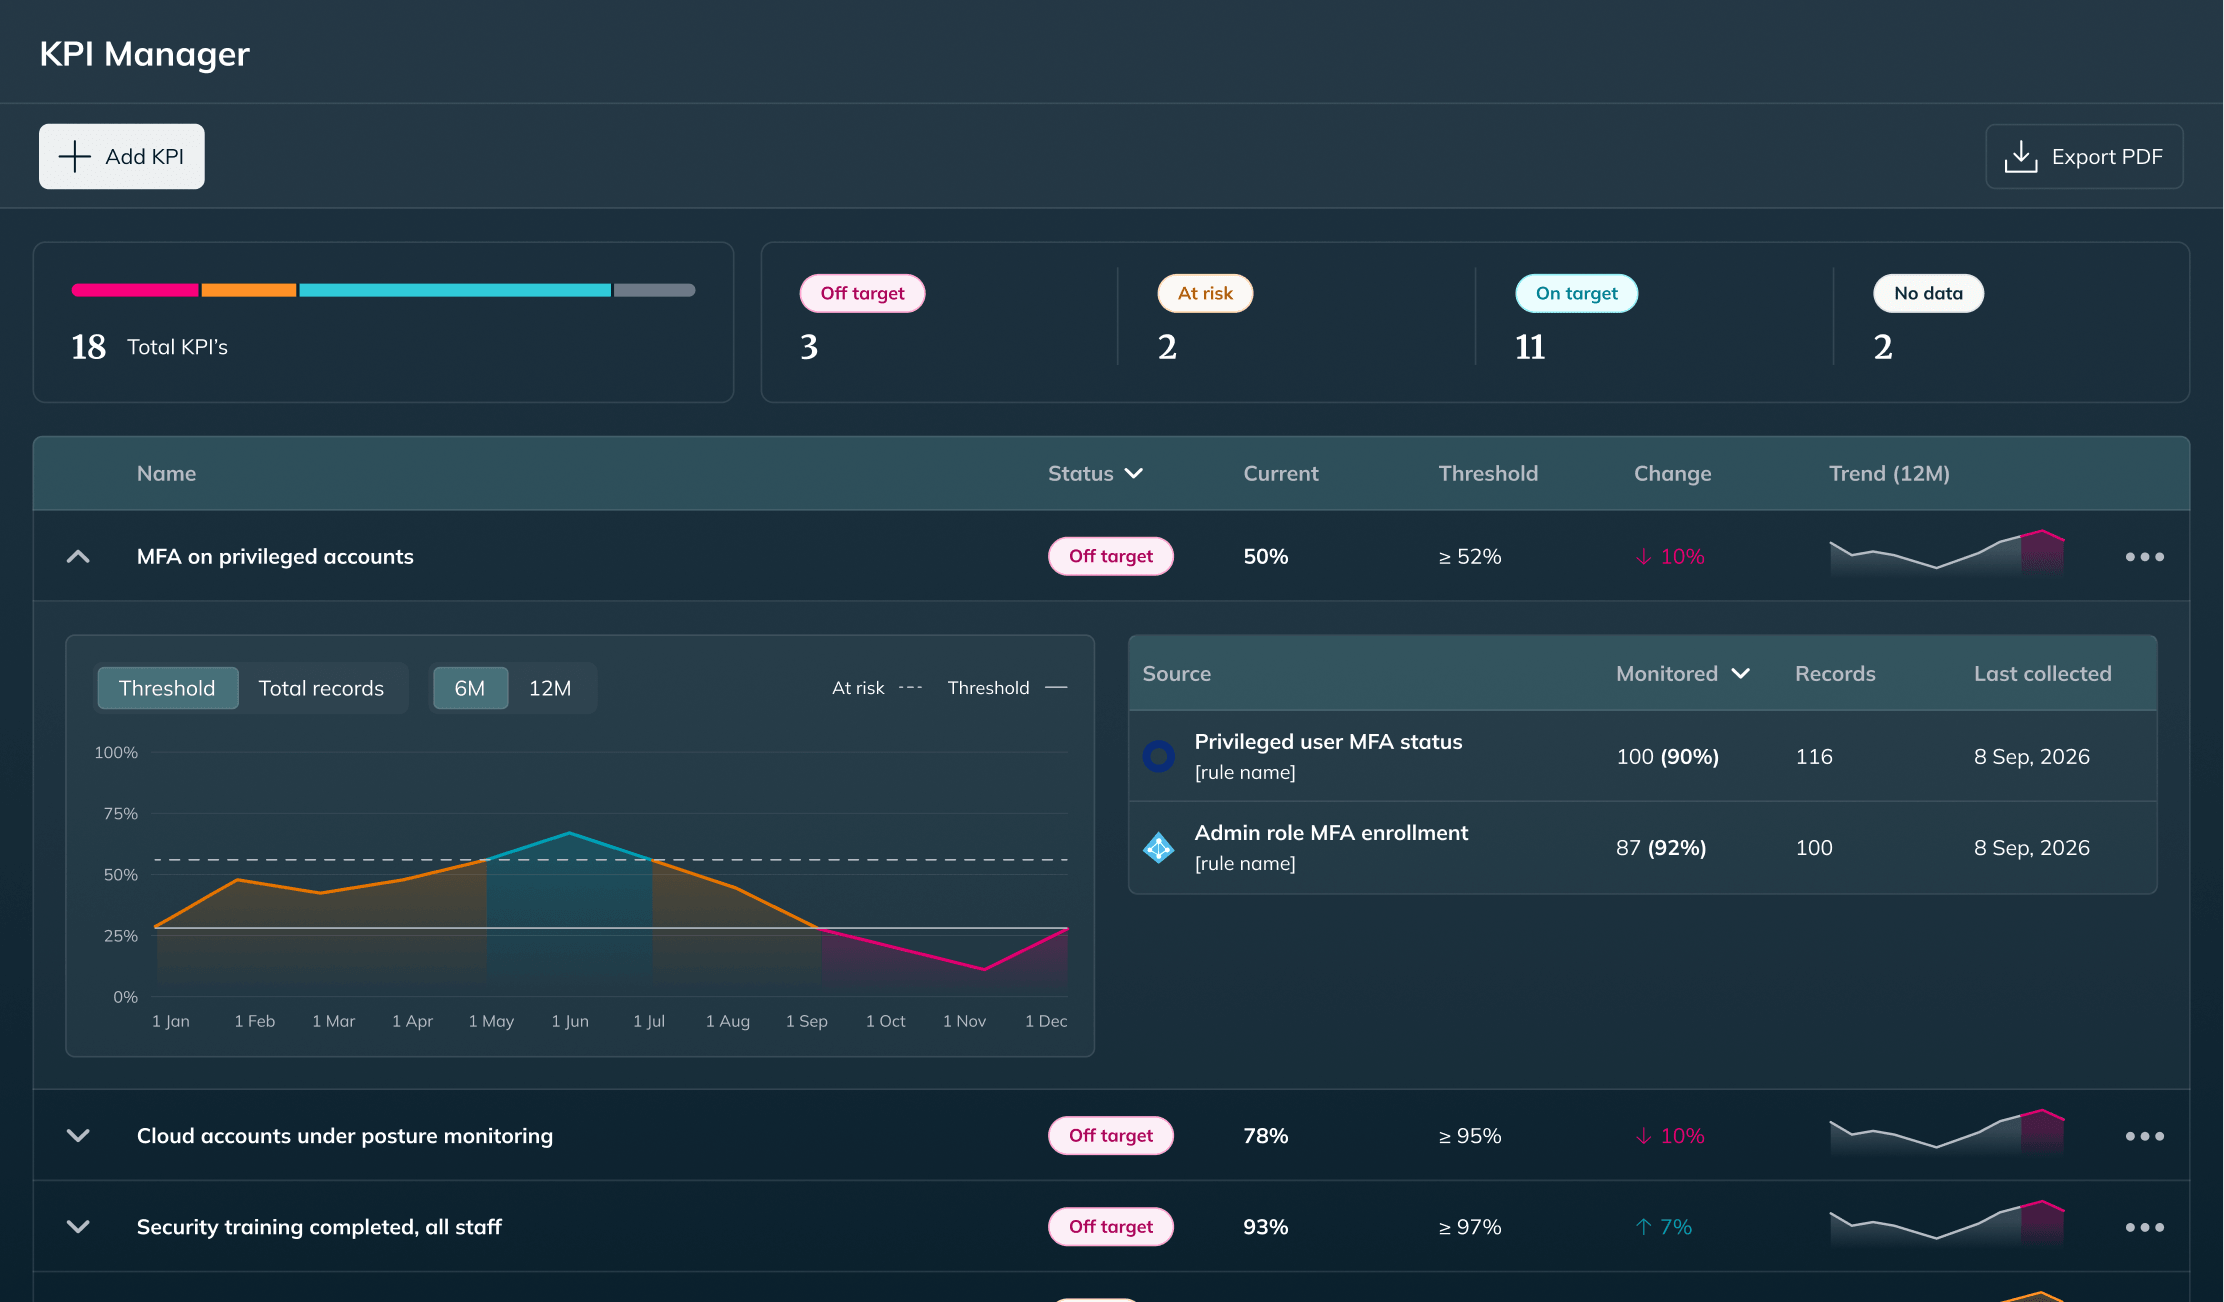
Your KPI board, always current
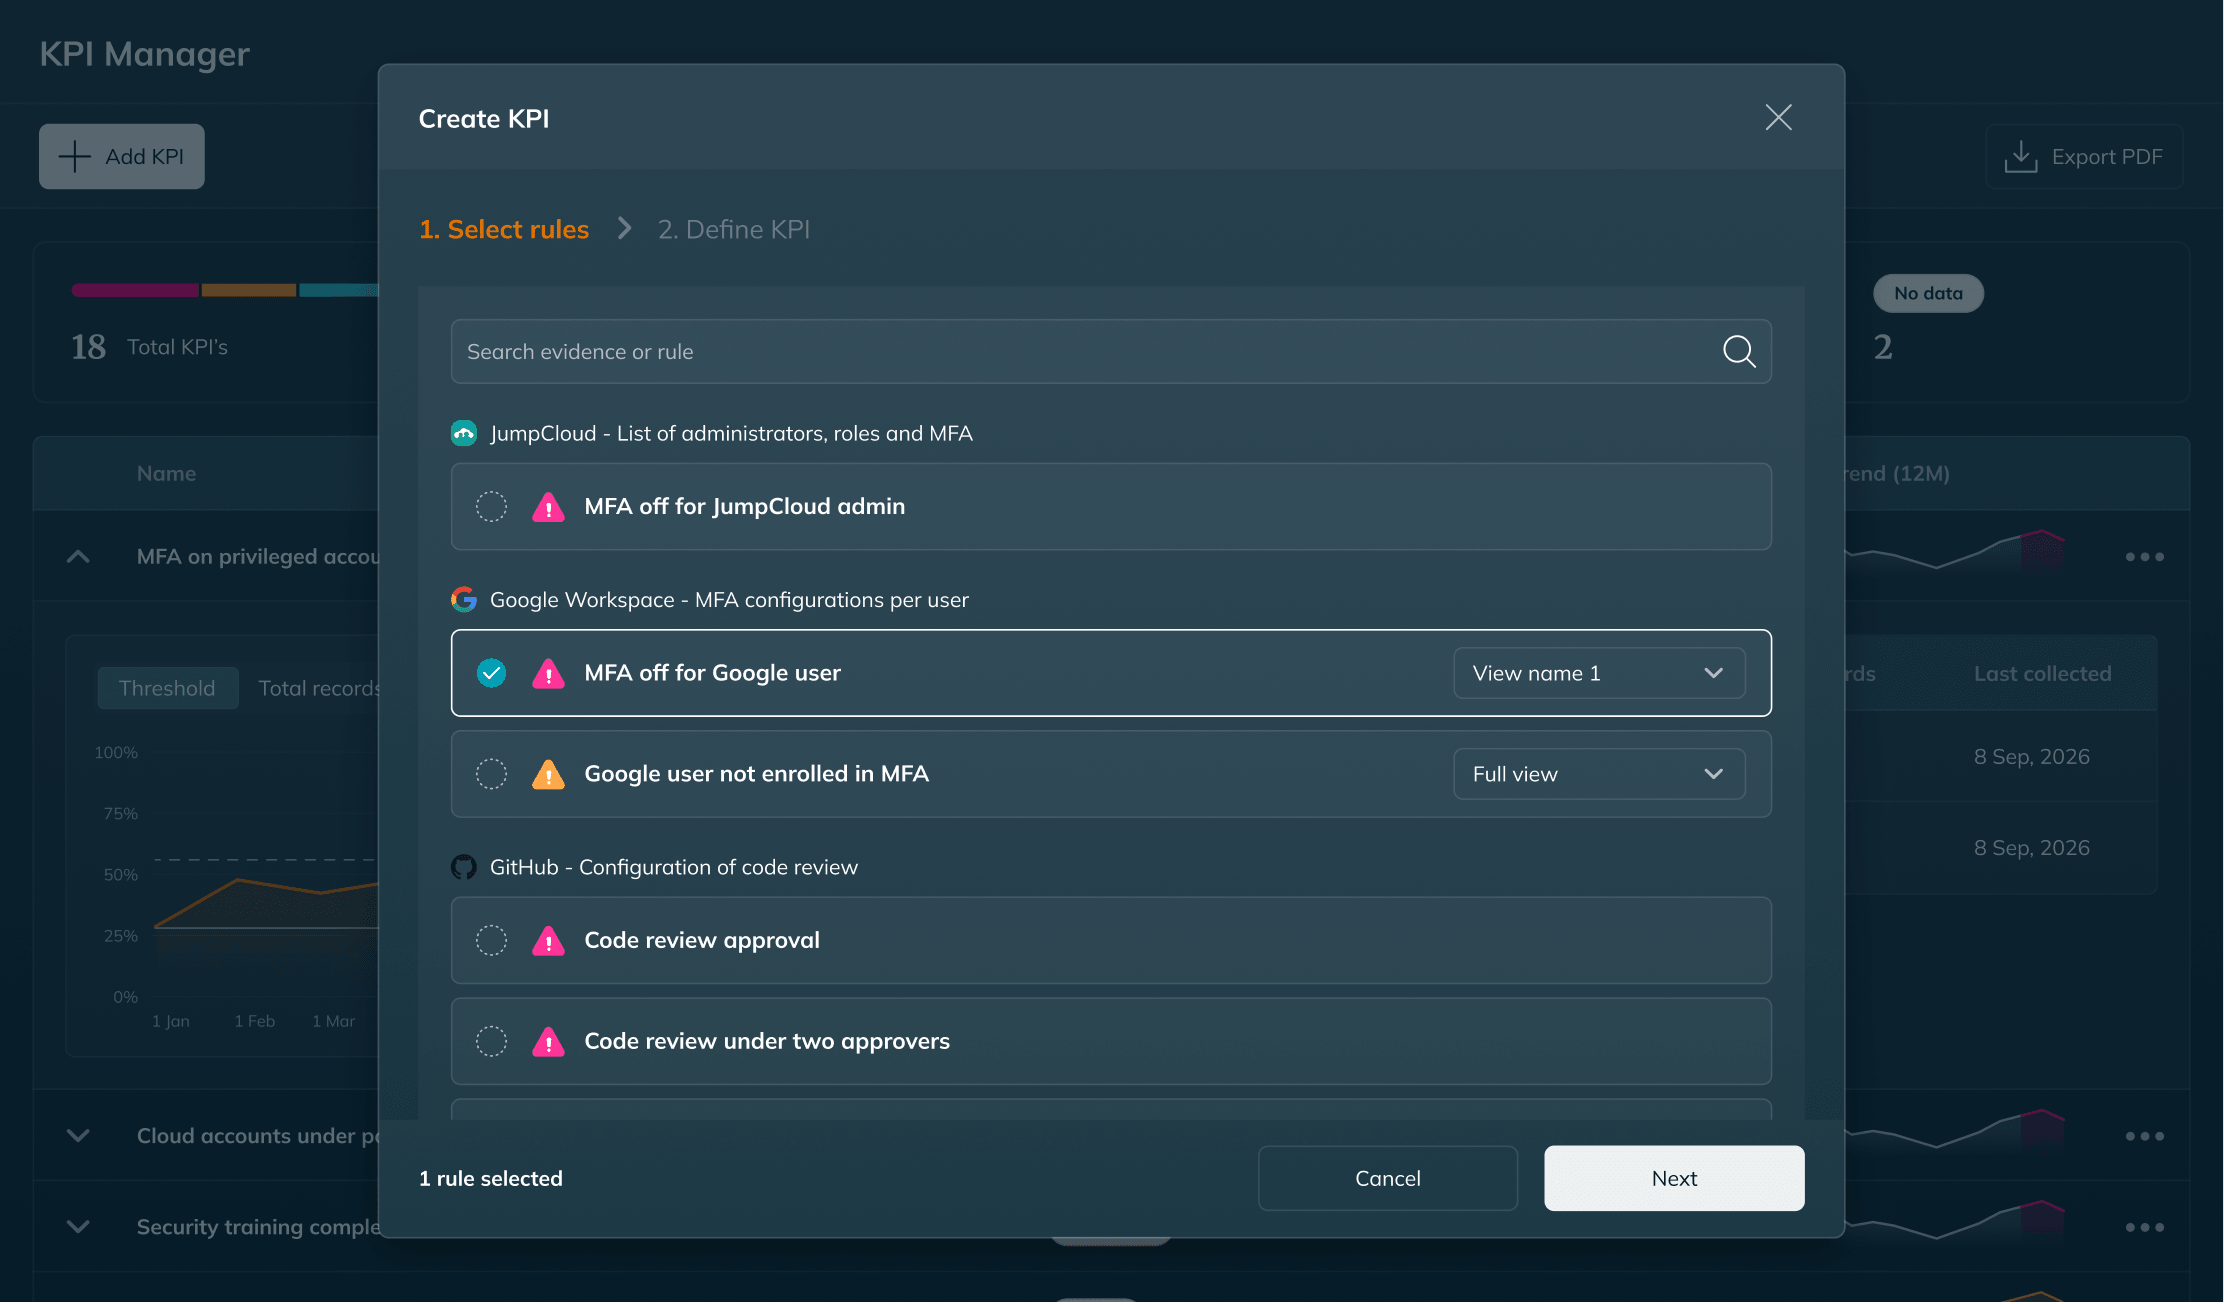
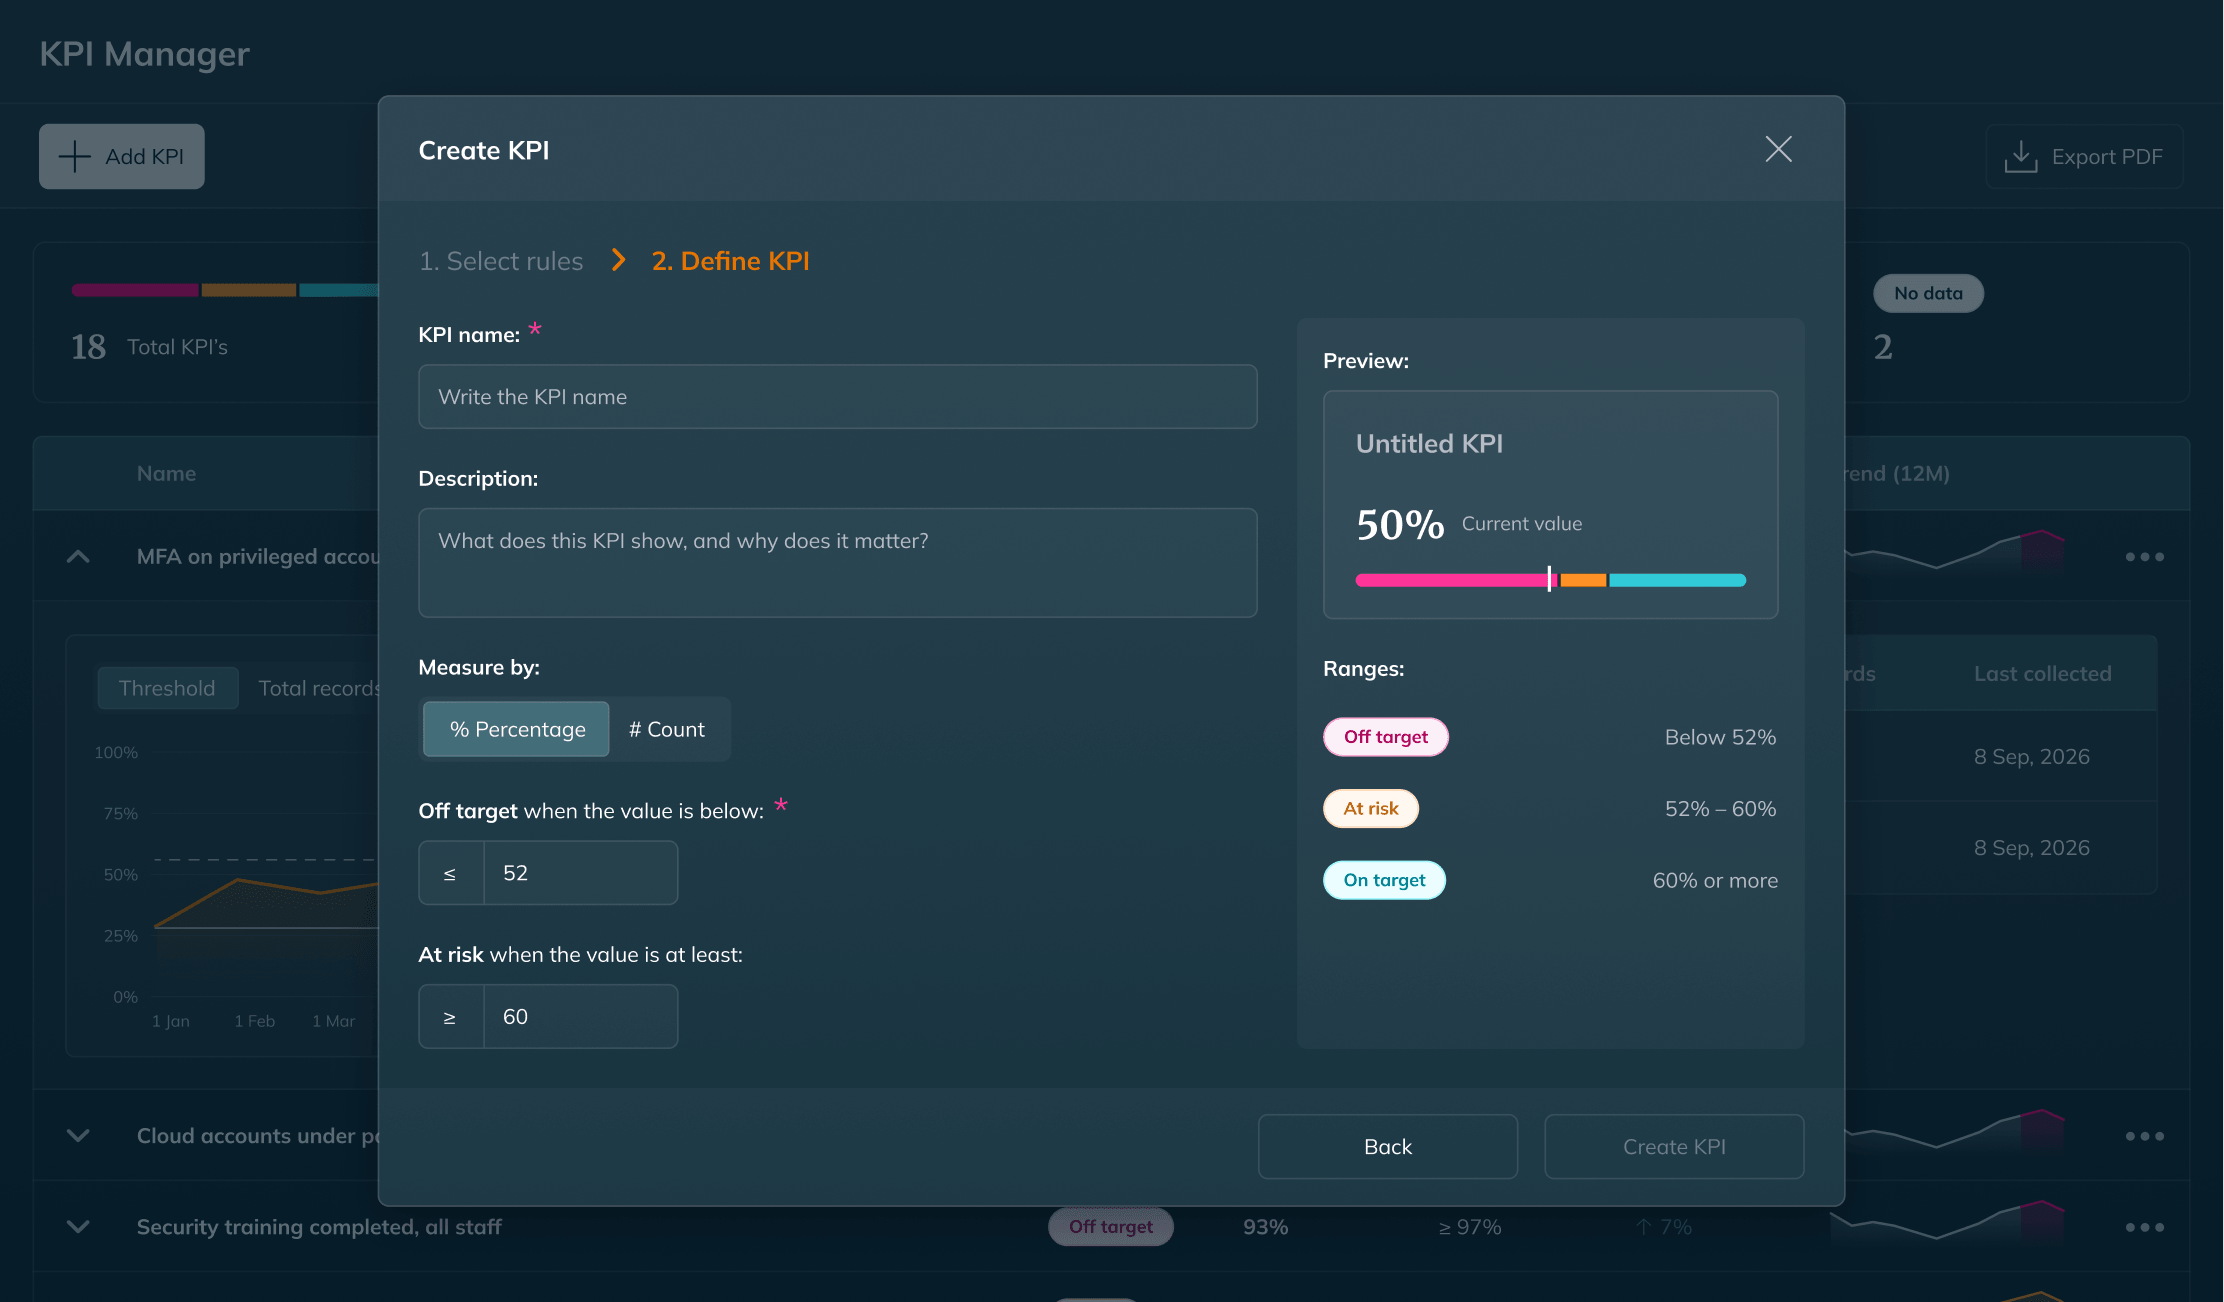

You assumed the coverage was there, but no one measured it
The breaches that end careers rarely come from a protection you never put in place. They come from the ones you assumed were working, right up until an MFA gap, a lapsed EDR agent, or a leaver who still had access proves otherwise.
Everyone owns a tool, nobody owns the number
Security, IT, HR, and engineering each run their own console, so every team can see its own slice while no one can see the number for the whole program.
The Security KPIs board deck
Your whole program, measured on your terms.
Frequently Asked Questions